

3D Secure Buyer's Guide
3D Secure buyer's guide: what to check before you pick a vendor
First up, if 3D Secure (3DS) is a fairly new concept to you, we’ve written an everything you need to know about 3DS guide to quickly get you up to speed.
Disclaimer: Evervault has its own 3DS solution, so we are biased, but all arguments made are rooted in logic and reality.
TL;DR: If you work with one PSP and have no plans to add any more, use their built-in 3DS. If you work with more than one PSP, or plan to, a standalone 3DS vendor, like Evervault, gives you one implementation, one set of results, and the ability to retry across PSPs without re-authenticating your customer.
When you're comparing providers, here are the key things you should consider.
Do you want to use PSPs built-in 3DS solutions or a standalone solution?
Do they run their own 3DS server?
How complex is it to integrate, set up, and debug?
What’s the end user experience like?
What options do you have to reduce friction?
Does the vendor reduce your PCI compliance scope?Built-in 3DS or standalone
Built-in 3DS or standalone
If you only work with one PSP, use their built-in 3DS. Adyen, Checkout.com, and Stripe can also automate authentication decisioning and retry logic based on issuer signals, which are especially powerful when combined with their fraud products.
The moment you work with more than one PSP, or plan to, built-in 3DS breaks down (see our guide on multi-PSP routing if you’re building this out). A 3DS authentication is tied to the PSP that processed it. If you retry a failed payment on a different PSP, you have to re-authenticate the customer from scratch. This hurts conversion rates.
Not only does re-authentication get in the way, you lose visibility too. Every PSP reports 3DS results in their own format, so building one view of your authentication performance means pulling and reconciling data from each of them yourself. A standalone vendor gives you that unified view by default, since every authentication, regardless of which PSP you route the payment through afterward, comes from the same place.
Standalone solutions typically come in two flavors: those that only do 3DS, and those that offer 3DS alongside other products, typically payment encryption or tokenization. All 3DS products are built to the same specification as per the latest protocol version, so everyone pretty much shares ~90% of the capability.
In our experience, these are the factors that matter when evaluating standalone 3DS solutions.
What to check when you compare 3DS vendors
Do they run their own 3DS server?
Some vendors build and run their own EMVCo-certified 3DS server. Others resell someone else's solution. You can check without taking their word for it. EMVCo publishes a public list of every company holding a 3DS license. Search the vendor's name and see if they have a Server license.
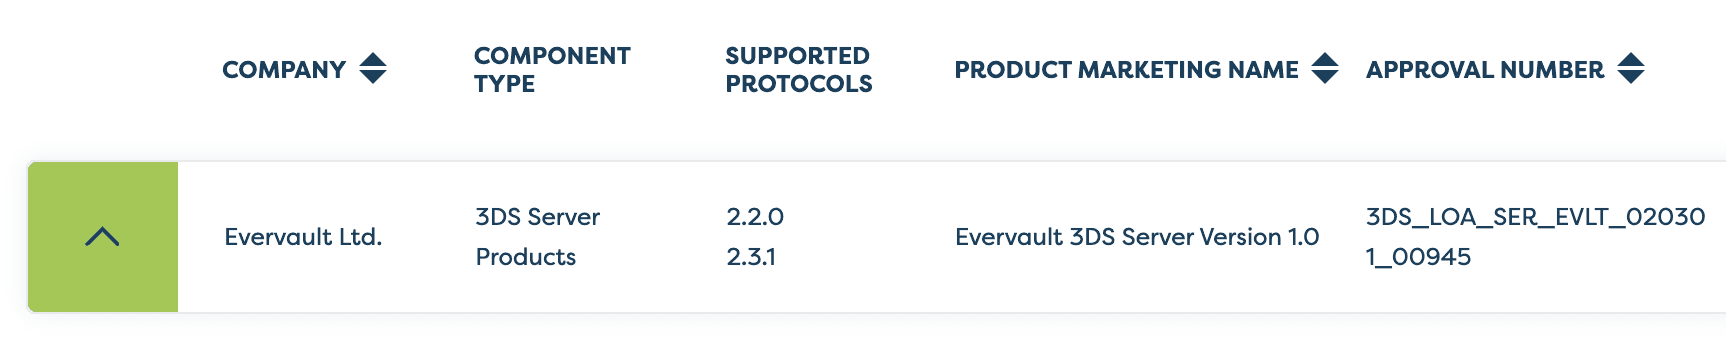
Source: EMVCo 3DS Approved Products Directory
Why this matters
If a vendor is reselling someone else's server, three things are true.
Product control is limited: You can't credibly promise what you don't build, so your feature requests are unlikely to be delivered.
In contrast, because Evervault owns its 3DS Server, we can develop features like fail-on-challenge that let customers in non-SCA-mandated regions attempt 3DS authentication to shift liability, but automatically terminate the authentication if the issuer steps up to a challenge. See our Flighthub case study for more info.
A reseller doesn't have that option, because the underlying server belongs to someone else. This extends to the latest EMVCo 3DS versions. A vendor with their own server decides when to certify against a new version. A reseller doesn’t.
Every hop adds latency and risk: Requests routed through a reseller go through an extra layer before reaching the actual 3DS server. Small delays compound. And when something breaks, the reseller's team has to first work out whether the problem is theirs or the underlying vendor's, then file a ticket and wait in someone else's support queue.
It’s more expensive: The reseller needs to take their cut.
How complex is it to integrate, set up, and debug?
Conforming to the 3DS spec and building a good implementation of it are different things. Two 3DS solutions can both be EMVCo-certified and still be wildly different products. Virtually all 3DS solutions default to exposing the entire spec and leaving you to figure it out. We think that’s a terrible developer experience, so we’ve abstracted as much of that complexity as possible but give you full customizability for more complex use-cases.
When assessing vendors, you want to be looking at:
Integration
With Evervault, integration takes less than an hour: one backend call, one frontend SDK load. This should be the standard, but it isn’t. Most other vendors hand you a multi-step flow you have to build and maintain across front- and back-end yourself.
See what an integration actually looks like
Integrating your average 3DS solution could take weeks, if not months, because they push the implementation burden onto you. This is the logic you’d need to write, debug, and maintain across both front-end and back-end.
You call the 3DS provider’s API to create the authentication request
It returns a
method_urlthat you pass to your frontend (this is technically optional but it provides a bunch of extra metadata, like device info, that helps improve authentication rates)You load an iframe with the
method_urlHandle the response to check if it will challenge (meaning the customer needs to complete authentication)
Redirect to the ACS (issuer) for the challenge
Capture the result and send it to the backend
Complete the flow with another API call (ARes, etc.)
In contrast, this is what it looks like with Evervault.
Call Evervault from your backend to create a 3DS session (this returns a
session_id)Load Evervault’s JavaScript SDK on your frontend using the
session_id
We handle everything else for you (loading the iframe with the method_url, managing redirects, handling challenges, etc.), including any spec changes as new protocols are released.
Orchestration logic
The 3DS specification is a huge 400+ page PDF and is inconsistent across card schemes. With Evervault, you describe what you want in plain language. (e.g., 'request an exemption', and we translate that into the correct network-specific request).
Most 3DS solutions kind of just implement the EMVCo spec as-is, leaving you to learn the spec and configure each request to its requirements.
What it looks like with most 3DS solutions
The authentication request (AReq) on its own has almost 100 fields on it, many of which can’t be understood intuitively. EMVCo (who made the spec) doesn’t provide an interactive reference site for the spec, so you have to work out of the PDF they provide.
There are also a lot of edge cases to manage with 3DS, especially for handling exemptions and non-standard flows (like corporate cards). On top of that, every card scheme (Visa, Mastercard, Amex) implements 3DS slightly differently (values, exemptions, protocol behavior, rules, etc.) so you have to build for each one individually. There might be some shared logic you can use, but at some point you have code that’s unique to each card brand.
That means you have to work with all of the complexities around AReqs (authentication requests), ARes (authentication responses), CReq (challenge requests), CRes (challenge responses), PReq (preparation requests), and PRes (preparation responses). And build logic that handles entire payloads (numeric codes, parameter mappings, network-specific logic, etc.). Even with some of the better APIs, you still end up with calls like this.
This is not ideal. Our belief is you should understand 3DS enough to know what you want to happen, and then express that intent with our product (e.g., "I want to request a 3DS exemption here") in plain language. We take that intent and translate it into the correct 3DS request for each network.
Error codes
The passing of 3DS spec complexity onto you is probably most destructive when it comes to debugging. Often you’re left to decode strings like N/A_06 or U_85 by searching documentation or the EMVCo spec itself. That's real engineering time lost on every failure investigation.
At Evervault, if the protocol definition is vague, we add our own English-language representation of what the code maps to, giving you extra context. We’ve been through the pain of deciphering EMVCo specifications. You shouldn’t have to.
Here are some examples of what we mean by human-readable error codes.
What Happened | Evervault | Without Evervault |
|---|---|---|
The issuer has rejected the authentication. Don’t attempt authorization. |
|
|
Authentication denied due to suspected fraud. |
|
|
The ACS is having technical issues and currently unavailable. |
|
|
The directory server encountered a system failure. |
|
|
Let’s explore the first example in the table to illustrate the friction involved.
A customer tries to pay, and 3DS authentication fails.
Why it failed: The issuer (the customer's bank) rejected the authentication because this card isn't allowed to make this kind of transaction. That could be because the bank has blocked online payments on the card, the cardholder has set controls that block this type of merchant, or the card can't be used in this country. It's the issuer's decision, not a problem with your setup, and the issuer is also asking you not to go ahead with authorization.
What to do about it: Don't retry. The same card will get the same answer, whether you try again on the same PSP or route it to a different one. The best next step is to ask the customer to use a different card or payment method, or to contact their bank if they want to use this one.
What to do about it: Don't retry. The same card will get the same answer, whether you try again on the same PSP or route it to a different one. The best next step is to ask the customer to use a different card or payment method, or to contact their bank if they want to use this one.
Most 3DS vendors
To work out what this means, someone on your team has to look up both codes in the EMVCo spec. Until then, they can't tell the difference between a card that's blocked for good from a card that's only blocked by a temporary error and that's worth retrying.
Evervault
See what happened at a glance. transaction-not-permitted tells you right away that this card won't work for this payment, so your checkout can prompt the customer for another payment method without anyone checking the spec.
Dig deeper when you need to. The raw codes are still there, each with a description, so your team has the full picture for investigating patterns or following up with an issuer.
What’s the end user experience like?
Some vendors, like Evervault, keep the 3DS challenge inside your checkout.
Others redirect the customer to a separate page or a new tab. A redirect breaks the customer's flow, adds a page load, and usually needs cookies to hold onto session state while the customer bounces back and forth. Browsers are getting more aggressive about blocking third-party cookies these days, so this can just break, mid-checkout, for no reason the customer will understand. EMVCo's own UX guidance actually recommends embedding the challenge inline for this reason, as it cuts cart abandonment.
Keep it inline instead, and the customer never leaves your page. It's just a modal you can theme with your own fonts, colors, and copy. You can also fingerprint the customer's device and hand that data to the issuer before they decide whether to challenge, which nudges the odds toward a frictionless approval in the first place.
What options do you have to reduce friction?
3DS is mandated in some markets so there’s not much you can do to reduce friction. But in markets where it’s not mandated, you can get many of the benefits of 3DS with zero friction.
Fail-on-challenge: This feature lets you attempt 3DS to secure liability shift, but if the issuer steps up to a challenge, it aborts the authentication request and proceeds to authorization. This is an awesome way to maximize the benefits of 3DS while ensuring zero friction.
The trade-off is if the issuer wants to challenge and you abort, you don't get liability shift on that transaction. But if zero friction is your priority, that's the whole point: you still get liability shift on everything that passes frictionlessly, and your customers never sit through a challenge screen.
Most vendors don’t support this, but it’s a favorite among our customers. Here’s how it works.
If the vendor does support fail-on-challenge, confirm they only charge per successful authentication (as Evervault does); otherwise, you'll be paying for attempts that never went anywhere.3DS data-only: Use this authentication method to send enriched data to issuers to increase acceptance rates by 2.2%+, without actually authenticating the customer, which means no fraud liability shift. With Visa transactions, this can lead to an 0.05% interchange fee reduction under Digital Commerce Authentication Program (DCAP).
Does the vendor reduce your PCI compliance scope?
A standalone 3DS provider needs the card number to run an authentication. It can't use the tokens your PSP gave you, because those tokens only work with that PSP. That leaves two options:
Handle raw card data yourself, which brings much of your infrastructure into PCI scope.
Use a third party to collect and secure it for you. That usually means one more vendor, one more integration, and one more copy of your card data to keep in sync with your 3DS provider.
The simpler setup is one vendor that both secures the card data and runs 3DS on it. That's how Evervault works. Card data is encrypted in the customer's browser before it reaches your servers, so raw card numbers never touch your infrastructure. The same encrypted card can then be authenticated with 3DS, routed to any PSP, and retried elsewhere, with no re-collection and no extra vendor in the middle.
If you're working out how to collect cards to enable multi-PSP routing without taking on a large compliance burden, we’ve written a four-part guide on the topic. It covers how PCI DSS applies to you, how the main card collection options compare, what the requirements look like in practice, and where Apple Pay, Google Pay, and network tokens fit.
One platform for 3DS and everything around it
Evervault runs its own EMVCo-certified 3DS server and secures your card data, so raw card numbers never touch your systems. You can authenticate once and route to any PSP.
Subscribe to our newsletter
Sign up to get access to the latest product insights.
" height="30px" id="PRZyQgeD6" width="49px"/></svg>)
" height="36px" id="bfXgof_0J" width="36px"/><path d="M 0 5.005 L 1.855 0.105 L 3.035 0.105 L 4.917 5.005 L 3.752 5.005 L 3.371 3.955 L 1.505 3.955 L 1.134 5.005 Z M 1.75 3.08 L 3.118 3.08 L 2.425 1.239 Z M 5.56 5.005 L 5.56 0.105 L 6.596 0.105 L 6.596 5.005 Z M 10.043 5.11 C 9.537 5.11 9.091 5.006 8.706 4.799 C 8.321 4.589 8.021 4.293 7.806 3.913 C 7.592 3.53 7.484 3.081 7.484 2.566 C 7.484 2.19 7.547 1.846 7.673 1.533 C 7.799 1.22 7.978 0.95 8.209 0.721 C 8.44 0.49 8.712 0.313 9.024 0.189 C 9.339 0.063 9.684 0 10.057 0 C 10.454 0 10.79 0.05 11.065 0.151 C 11.34 0.251 11.588 0.392 11.807 0.574 L 11.282 1.425 C 11.14 1.285 10.97 1.18 10.774 1.11 C 10.581 1.04 10.365 1.005 10.127 1.005 C 9.884 1.005 9.666 1.041 9.472 1.113 C 9.281 1.185 9.118 1.289 8.982 1.425 C 8.849 1.558 8.747 1.72 8.674 1.911 C 8.604 2.1 8.569 2.314 8.569 2.552 C 8.569 2.878 8.632 3.157 8.758 3.388 C 8.887 3.617 9.069 3.793 9.304 3.917 C 9.542 4.04 9.826 4.102 10.155 4.102 C 10.384 4.102 10.608 4.067 10.827 3.997 C 11.049 3.927 11.257 3.815 11.453 3.661 L 11.929 4.533 C 11.698 4.71 11.428 4.851 11.117 4.956 C 10.807 5.059 10.449 5.11 10.043 5.11 Z M 12.677 5.005 L 12.677 0.105 L 14.577 0.105 C 14.936 0.105 15.255 0.168 15.533 0.294 C 15.81 0.418 16.028 0.598 16.187 0.836 C 16.346 1.072 16.425 1.356 16.425 1.687 C 16.425 2.025 16.352 2.312 16.205 2.548 C 16.058 2.781 15.844 2.96 15.564 3.083 C 15.286 3.205 14.949 3.265 14.553 3.265 L 13.713 3.265 L 13.713 5.005 Z M 13.713 2.394 L 14.535 2.394 C 14.803 2.394 15.012 2.339 15.162 2.23 C 15.313 2.12 15.389 1.946 15.389 1.708 C 15.389 1.468 15.312 1.289 15.158 1.173 C 15.004 1.056 14.799 0.998 14.542 0.998 L 13.713 0.998 Z M 16.454 5.005 L 18.309 0.105 L 19.489 0.105 L 21.372 5.005 L 20.206 5.005 L 19.825 3.955 L 17.959 3.955 L 17.588 5.005 Z M 18.204 3.08 L 19.573 3.08 L 18.88 1.239 Z" fill="rgb(255, 255, 255)" height="5.110000000000001px" id="iLW2hnaLh" transform="translate(7.313 9.995)" width="21.371599655151368px"/><path d="M 1.918 5.11 C 1.556 5.11 1.205 5.058 0.864 4.953 C 0.524 4.848 0.236 4.695 0 4.494 L 0.493 3.717 C 0.601 3.824 0.733 3.917 0.889 3.994 C 1.048 4.071 1.216 4.13 1.393 4.172 C 1.573 4.212 1.749 4.232 1.921 4.232 C 2.188 4.232 2.403 4.185 2.569 4.092 C 2.735 3.998 2.817 3.862 2.817 3.682 C 2.817 3.537 2.759 3.417 2.643 3.322 C 2.526 3.224 2.309 3.13 1.992 3.042 L 1.543 2.916 C 1.051 2.778 0.697 2.591 0.479 2.356 C 0.262 2.12 0.154 1.834 0.154 1.498 C 0.154 1.279 0.2 1.078 0.29 0.896 C 0.381 0.714 0.509 0.557 0.672 0.424 C 0.838 0.291 1.032 0.188 1.256 0.116 C 1.483 0.041 1.728 0.004 1.992 0.004 C 2.348 0.004 2.68 0.056 2.986 0.161 C 3.293 0.264 3.543 0.405 3.734 0.585 L 3.223 1.337 C 3.13 1.244 3.017 1.163 2.884 1.096 C 2.753 1.028 2.611 0.975 2.457 0.938 C 2.303 0.898 2.148 0.879 1.992 0.879 C 1.823 0.879 1.675 0.902 1.547 0.949 C 1.421 0.993 1.323 1.058 1.253 1.145 C 1.183 1.229 1.148 1.33 1.148 1.449 C 1.148 1.54 1.172 1.618 1.221 1.684 C 1.273 1.747 1.358 1.806 1.477 1.862 C 1.598 1.918 1.764 1.976 1.974 2.037 L 2.436 2.174 C 2.921 2.316 3.274 2.497 3.493 2.716 C 3.712 2.935 3.822 3.22 3.822 3.57 C 3.822 3.873 3.745 4.142 3.591 4.375 C 3.439 4.606 3.22 4.787 2.933 4.918 C 2.648 5.046 2.31 5.11 1.918 5.11 Z M 6.984 5.11 C 6.611 5.11 6.266 5.046 5.948 4.918 C 5.631 4.787 5.356 4.606 5.122 4.375 C 4.889 4.144 4.707 3.873 4.576 3.563 C 4.448 3.253 4.384 2.917 4.384 2.555 C 4.384 2.191 4.448 1.854 4.576 1.543 C 4.707 1.233 4.889 0.962 5.122 0.732 C 5.356 0.5 5.631 0.321 5.948 0.192 C 6.266 0.064 6.611 0 6.984 0 C 7.358 0 7.702 0.065 8.017 0.196 C 8.334 0.327 8.61 0.509 8.843 0.742 C 9.079 0.975 9.262 1.247 9.392 1.557 C 9.523 1.865 9.588 2.198 9.588 2.555 C 9.588 2.917 9.523 3.253 9.392 3.563 C 9.262 3.873 9.079 4.144 8.843 4.375 C 8.61 4.606 8.334 4.787 8.017 4.918 C 7.702 5.046 7.358 5.11 6.984 5.11 Z M 6.984 4.137 C 7.201 4.137 7.402 4.1 7.586 4.025 C 7.771 3.95 7.932 3.844 8.069 3.706 C 8.207 3.566 8.313 3.4 8.388 3.206 C 8.465 3.012 8.503 2.795 8.503 2.555 C 8.503 2.235 8.437 1.958 8.304 1.722 C 8.171 1.484 7.99 1.3 7.761 1.169 C 7.533 1.038 7.274 0.973 6.984 0.973 C 6.77 0.973 6.569 1.01 6.382 1.085 C 6.198 1.16 6.037 1.266 5.899 1.403 C 5.764 1.541 5.658 1.708 5.581 1.904 C 5.506 2.098 5.469 2.315 5.469 2.555 C 5.469 2.875 5.535 3.153 5.668 3.391 C 5.801 3.627 5.982 3.81 6.211 3.941 C 6.44 4.072 6.697 4.137 6.984 4.137 Z M 12.801 5.11 C 12.294 5.11 11.849 5.006 11.464 4.799 C 11.079 4.588 10.779 4.293 10.564 3.913 C 10.35 3.53 10.242 3.081 10.242 2.566 C 10.242 2.19 10.305 1.846 10.431 1.533 C 10.557 1.22 10.736 0.95 10.967 0.721 C 11.198 0.49 11.47 0.313 11.782 0.189 C 12.097 0.063 12.441 0 12.815 0 C 13.211 0 13.547 0.05 13.823 0.15 C 14.098 0.251 14.345 0.392 14.565 0.574 L 14.04 1.424 C 13.897 1.284 13.728 1.179 13.532 1.11 C 13.339 1.04 13.123 1.005 12.885 1.005 C 12.642 1.005 12.424 1.041 12.23 1.113 C 12.039 1.185 11.876 1.289 11.74 1.424 C 11.607 1.557 11.505 1.72 11.432 1.911 C 11.362 2.1 11.327 2.313 11.327 2.552 C 11.327 2.878 11.39 3.157 11.516 3.388 C 11.645 3.617 11.827 3.793 12.062 3.916 C 12.3 4.04 12.584 4.102 12.913 4.102 C 13.141 4.102 13.365 4.067 13.585 3.997 C 13.806 3.927 14.015 3.815 14.211 3.661 L 14.687 4.532 C 14.456 4.71 14.186 4.851 13.875 4.956 C 13.565 5.059 13.207 5.11 12.801 5.11 Z M 16.851 5.005 L 16.851 4.312 L 17.897 3.363 C 18.224 3.067 18.482 2.819 18.671 2.618 C 18.862 2.415 18.998 2.235 19.077 2.079 C 19.159 1.923 19.199 1.765 19.199 1.607 C 19.199 1.373 19.121 1.192 18.965 1.064 C 18.809 0.936 18.588 0.871 18.303 0.871 C 18.089 0.871 17.882 0.912 17.684 0.994 C 17.488 1.073 17.315 1.191 17.166 1.348 L 16.805 0.598 C 17.02 0.405 17.266 0.257 17.544 0.154 C 17.824 0.051 18.111 0 18.405 0 C 18.76 0 19.069 0.062 19.332 0.185 C 19.596 0.309 19.799 0.483 19.941 0.707 C 20.086 0.929 20.158 1.188 20.158 1.484 C 20.158 1.687 20.119 1.886 20.039 2.082 C 19.96 2.276 19.819 2.494 19.616 2.737 C 19.415 2.98 19.132 3.274 18.765 3.619 L 18.195 4.151 L 20.288 4.151 L 20.288 5.005 Z" fill="rgb(255, 255, 255)" height="5.110000000108034px" id="Vv9VsTrSa" transform="translate(7.854 21.995)" width="20.287900848388674px"/><path d="M 0 1 L 0 0 L 22 0 L 22 1 Z" fill="rgb(255, 255, 255)" height="1px" id="TKS4yrk0q" transform="translate(7 18)" width="22px"/></svg>)
© 2026 Evervault Inc. All rights reserved.